Bridging frameworks: How HAIP 2.0 supports interoperability with the EU AI Act


This blog article is part of a series on the Hiroshima AI Process (HAIP) Reporting Framework. The series explores different dimensions of the framework, its role in supporting trustworthy AI, and insights emerging from reports submitted by participating organisations.
In May 2026, the OECD launched version 2.0 of the Hiroshima AI Process (HAIP) reporting framework, on the margins of France’s G7 presidency. The voluntary reporting framework provides a global, public and comparable tool for organisations across the AI value chain to report on their actions to promote trustworthy AI. Participation enables organisations to showcase their AI governance and risk management practices, strengthen transparency, contribute to a shared understanding of how AI risks are managed, and support greater consistency across the global AI governance landscape.
HAIP differs from the EU’s AI Act, and the associated General-Purpose AI Code of Practice (CoP) in being both voluntary and public. Rather than replacing EU regulation, the HAIP 2.0 Framework can complement it. Both frameworks show significant areas of convergence and overlap. For instance, information and evidence prepared for EU AI Act compliance can serve as an information base to file a HAIP report, thereby facilitating reporting for EU companies.
This blog article explores how HAIP 2.0 and the EU instruments intersect, where they diverge, and why their complementarity matters for effective AI governance.
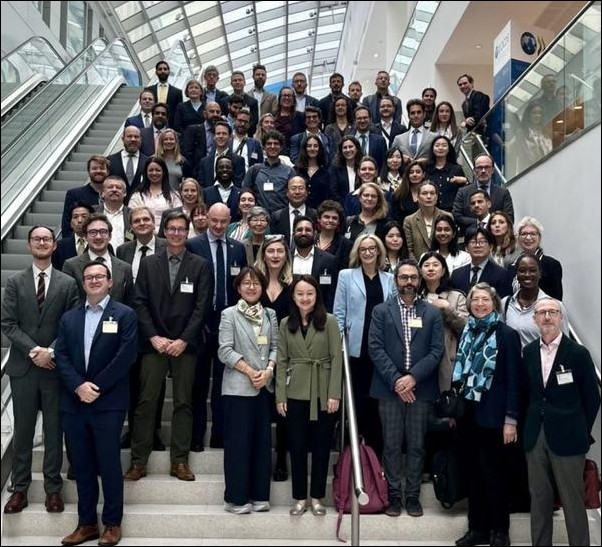
5th Plenary Meeting of the Global Partnership on AI (GPAI), OECD, June 2026
HAIP 2.0 is aligned with the EU regulatory framework, allowing organisations to leverage existing compliance efforts
HAIP 2.0 is a structured reporting framework for organisations operating structured reporting framework for organisations operating across the value chain of advanced AI systems, including model developers, application providers and deployers. In June 2026, the Centre pour la Sécurité de l’IA (CeSIA) conducted a detailed mapping exercise and found substantial overlap between HAIP 2.0 and the EU AI Act and CoP: 80% of HAIP 2.0’s questions refer to requirements covered by the EU regime, with 58% of these having strong or partial alignment.
This is good news for companies that already comply with EU obligations: information and evidence prepared for EU AI Act compliance can serve as an information base to file a HAIP report. A signatory to the CoP can reuse much of the same underlying evidence to satisfy HAIP’s reporting questions. For companies operating in the EU market, submitting a HAIP report also provides an opportunity to make their practices visible through a common international framework, compare their approaches with those of peers and demonstrate their commitment to trustworthy AI to a wider set of stakeholders.
Rather than creating a parallel set of requirements, HAIP 2.0 builds on existing governance efforts to create a global transparency standard. HAIP 2.0 comprises 31 reporting questions. When these questions are mapped against the EU AI Act and CoP, the degree of alignment is significant. For example, HAIP’s question on systemic risk transparency aligns with the CoP’s commitment on safety and security model reports. Similarly, HAIP’s questions on capability and propensity thresholds align with the CoP’s provisions identifying model capabilities, propensities and affordances as sources of systemic risk.
Alongside commonalities, HAIP 2.0 and the EU framework each bring unique and complementary value to global AI governance
The information required under HAIP 2.0 and the EU instruments overlaps significantly, but they also serve distinct purposes. HAIP is a voluntary framework centred on public transparency, global reach and comparability, while the EU framework is binding and enforceable within the EU.
HAIP 2.0’s added value lies in public transparency
One of the HAIP reporting framework’s most significant value added and marked distinctions is that HAIP reports submitted to the OECD are published openly on the OECD.AI Policy Observatory, making them accessible to researchers, civil society, media, public authorities and other industry players. The EU framework follows a different disclosure model. Most EU AI Act reporting, such as technical documentation, conformity assessments and post-market monitoring reports, stays private, submitted only to the EU AI Office, downstream providers or national competent authorities. Even the CoP’s model reports are confidential, with only summarised versions published. Beyond its public transparency, HAIP is also voluntary and open to organisations based in OECD member countries, GPAI members, and jurisdictions adhering to the OECD Recommendation on Artificial Intelligence.
HAIP does not substitute for EU reporting: where the AI Act and CoP apply, they still set the binding requirement. Instead, HAIP adds a voluntary public-transparency layer available both to organisations operating in the EU and to eligible organisations elsewhere. For companies in the EU, HAIP can increase the visibility and comparability of work already undertaken as part of compliance with the EU AI Act. It allows them to present relevant information to an international audience through a common reporting structure, demonstrate their governance practices publicly and contribute to the exchange of good practices across jurisdictions.
The EU AI governance architecture
Turning to the EU’s reporting regime, it is worth recalling that these mechanisms align directly with the EU AI Act’s requirements. The EU AI Act establishes requirements for several operators across the AI value chain, including providers and deployers, with separate obligations for providers of general-purpose AI models. The applicable requirements depend on the actor’s role and the type and risk classification of the AI system or model concerned.
The CoP only applies to general-purpose AI providers. Its Transparency and Copyright chapters address all providers of general-purpose AI models, while its Safety and Security chapter is further limited to those carrying systemic risk.
Like HAIP, adherence to the CoP is voluntary. Unlike HAIP, however, the CoP is designed to help providers demonstrate legal compliance with binding obligations under the EU AI Act. It focuses solely on individual disclosure, asking signatories to publish their own safety and security frameworks and reports, on their own platforms, with no obligation to publish in any language other than their own. This makes it harder to compare and contrast across reports.
HAIP reaches different actors across the AI value chain through a global reporting framework
HAIP 2.0 features a role-based architecture, distinguishing between model developers, application providers, deployers and small and medium-sized enterprises (SMEs). For efficiency, each role gets routed through tailored questions. This allows HAIP 2.0 to capture information from different parts of the AI value chain through a single reporting framework.
HAIP is built for comparability and information sharing. Its format enables benchmarking across companies and reports thanks to a structured approach: checkboxes, yes/no gates and conditional follow-ups.
To favour interoperability, reduce fragmentation and lower the reporting burden, HAIP 2.0 reuses terminology from existing frameworks, including the EU regulatory framework, the NIST AI Risk Management Framework and ISO/IEC 42001, among others. HAIP 2.0 also incorporates elements of the New Delhi Frontier AI Impact Commitments, with questions geared to multilingual evaluation and anonymised usage statistics.
Whereas the EU AI Act and CoP are, by design, EU-centric instruments, HAIP 2.0 acts as a bridge between regional and global governance efforts, by embedding concepts and commitments developed across different jurisdictions.
At the launch of the augmented HAIP 2.0 reporting framework in May 2026, more than 50 organisations pledged to report under the revised framework, arguably pointing to an appetite for a global and transparent reporting standard. But it is important to remember that signing a pledge is a much lighter commitment than filing a full report. The real test of HAIP 2.0’s will be the number of organisations to follow through with actual disclosures and keep them updated.
Two complementary approaches to trust
Despite these commonalities, it is important not to lose sight of the fundamental differences between the frameworks. The EU AI Act is a binding regulation, enforced by the EU AI Office, national competent authorities and sanctions under Article 99. These sanctions can reach up to EUR 35 million or 7% of global annual turnover, whichever is higher, for prohibited practices, and up to EUR 15 million or 3% of global annual turnover for other non-compliance.
HAIP, by contrast, is voluntary. An organisation that does not participate is not subject to fines. Incentives to report are instead linked to public transparency, reputational value, international comparability and the exchange of good practices. HAIP could contribute to shaping future reporting obligations and international norms.
The mapping of HAIP 2.0 against the EU AI Act and the associated General-Purpose AI Code of Practice shows that these frameworks are complementary layers in a global AI governance stack. It also shows that any organisation that has followed the EU’s regime can use reports submitted under this regime as source material when filing a HAIP report, thereby reducing duplication of effort.
Methodological note
The comparative mapping developed by the Centre pour la Sécurité de l’IA (Jonathan Salter and Charbel-Raphaël Ségerie) assesses each of the 31 HAIP 2.0 reporting questions separately against the EU AI Act and the General-Purpose AI Code of Practice.
Each question was evaluated using four alignment categories: Strong, where a directly applicable and binding provision substantially matches the content of the HAIP question; Partial, where a binding provision overlaps with the question but is limited in scope (for example, applying only to General-Purpose AI models with systemic risk, requiring confidential rather than public disclosure, or addressing only part of the reporting requirement); Weak/Indirect, where the relationship relies on non-binding guidance, recitals, encouraged practices, or general references to standards; and No coverage, where no equivalent provision could be identified.
The assessment was conducted by applying four analytical tests to each HAIP question: (i) whether the substantive content aligns with the corresponding EU provision; (ii) whether the obligation is legally binding or voluntary; (iii) which categories of actors are covered; and (iv) the extent to which the required information is publicly disclosed or remains confidential. The reported alignment percentages reflect CeSIA’s independent comparative analysis and should not be interpreted as an official assessment by the OECD or the European Union.